
Snyk
Developer-first AI security platform — DeepCode AI SAST, SCA, container, IaC, and AI Security Fabric
Gallery
4 items
About Snyk
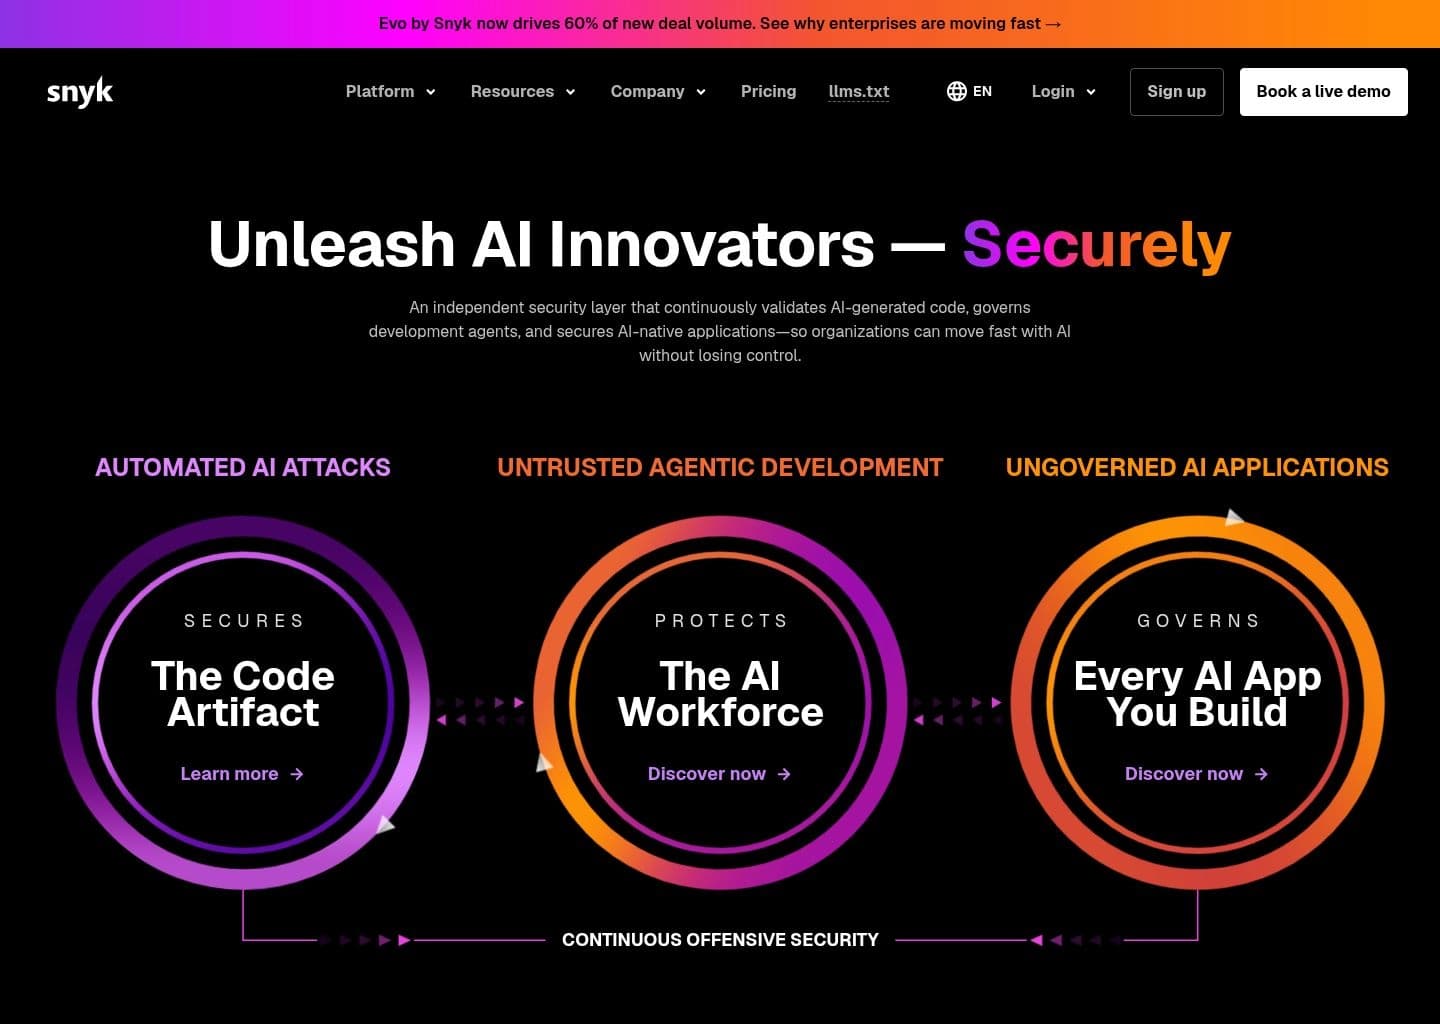
Testing Snyk across developer Git workflows demonstrated why it is the developer-first AppSec standard: its DeepCode AI scans open-source libraries, container images, and Kubernetes infrastructure-as-code with instant 1-click pull request fixes. It fixes vulnerabilities right inside IDEs and PRs. Large enterprise monorepos with hundreds of legacy dependencies can initially surface thousands of low-severity alerts that require triage filters. Offering a capable free tier and enterprise plans, it is an essential DevSecOps companion for modern engineering teams.
Snyk is the world's leading developer-first application security platform, founded in 2015 in London with offices in Boston, used by 2,500+ paying customers including Google, Salesforce, Intuit, and Atlassian. With $530M+ in total funding at an $8.6B valuation and $407M+ in 2025 revenue, Snyk has established itself as the benchmark for security that developers actually use \u2014 embedding vulnerability detection and AI-powered auto-fix directly into the developer\u2019s natural workflow: their IDE, their Git repository, and their CI/CD pipeline.
Snyk\u2019s platform spans five security products \u2014 Snyk Code (SAST), Snyk Open Source (SCA), Snyk Container, Snyk IaC, and Snyk API \u2014 all powered by DeepCode AI, Snyk\u2019s proprietary AI engine that combines symbolic AI with machine learning trained on billions of lines of code to detect vulnerabilities with higher accuracy and lower false positives than traditional rule-based scanners. Snyk Agent Fix generates one-click remediation patches in the IDE, Snyk Assist explains vulnerabilities in natural language, and Snyk Guard enforces adaptive security policies across both AI-generated and human-written code. In 2026, Snyk repositioned its platform as the \u201cAI Security Fabric\u201d \u2014 covering security for AI-generated code, agentic workflows, and LLM-integrated applications.
Snyk is the right choice for developer teams and DevSecOps organizations that want security embedded in the developer workflow rather than bolted on afterward \u2014 particularly fast-moving engineering teams, startups scaling their security posture, and enterprises wanting to shift security left without slowing development velocity.
Key Features
- Snyk Code — AI-powered SAST using DeepCode AI with one-click fix suggestions directly in the IDE
- Snyk Open Source — SCA scanning for vulnerabilities in open-source dependencies with license compliance
- Snyk Container — container image and registry scanning for OS and application layer vulnerabilities
- Snyk IaC — infrastructure-as-code scanning for Terraform, CloudFormation, Kubernetes, and Helm misconfigurations
- Snyk API — dynamic API security testing for web applications and APIs
- Snyk Agent Fix — AI agent that automatically generates and applies code patches for detected vulnerabilities
- Snyk Assist — AI developer assistant that explains vulnerabilities and suggests remediation in context
- Snyk Guard — adaptive security guardrails that enforce policies across AI-generated and human-written code
- IDE integrations for VS Code, JetBrains, Eclipse, and more — real-time vulnerability feedback while coding
- CI/CD integrations with GitHub, GitLab, Bitbucket, Jenkins, CircleCI, and all major pipelines
Pros
- Developer-first design — real-time IDE feedback and one-click fixes where developers already work
- DeepCode AI generates remediation patches automatically — not just detection but actual fix suggestions
- All five security products (Code, Open Source, Container, IaC, API) in one subscription at every tier
- 1B+ security tests/month across 2,500+ customers including Google, Salesforce, and Intuit
- Gartner Magic Quadrant Leader for Application Security Testing (2025)
- $407M+ revenue, $8.6B valuation, $530M+ raised — financially robust and growing
- Snyk Guard and AI Security Fabric (2026) addresses AI-generated code vulnerabilities proactively
Cons
- Per-developer pricing scales painfully for larger teams — becomes expensive beyond 50-100 developers
- Enterprise features require custom pricing negotiations with sales team
- False positives require more manual triage than ideal
- Free plan limited to open-source projects only — private repo scanning requires paid plan
- Some advanced features have a steep learning curve for developer teams new to AppSec
Pricing
Snyk offers a free tier for open-source projects with limited test counts \u2014 a genuine starting point for individual developers and small teams working on public repositories.
Team plan at $25/developer/month (minimum 5 developers, up to 10 developers) includes all five security products (Code, Open Source, Container, IaC, API) with prioritized vulnerability remediation, compliance reporting, and integration with enterprise security tools.
Enterprise plan at custom pricing (contact sales) adds SSO/SAML, advanced analytics and reporting dashboards, SBOM generation, compliance frameworks (CIS, PCI, ISO, HIPAA, SOC 2), Snyk Guard for adaptive policy enforcement, dedicated customer success, and API access for custom integrations. Note: per-developer pricing scales quickly and can become expensive for teams beyond 50-100 developers.
Claim Verified Creator Badge
Are you the founder of Snyk? Display this listing's verified badge on your website to show your customers that your product has been vetted and listed on AI Central Resources.
<a href="https://www.aicentralresources.com/tool/snyk" target="_blank" rel="noopener">
  <img src="https://www.aicentralresources.com/badges/featured-badge-dark.svg" alt="Featured on AICentralResources" width="200" height="54" style="border: none;" />
</a>
* Place this HTML snippet in your website's footer, landing page, or press section. This creates a search-friendly backlink directly to your verification page.
Connect with Snyk
Frequently Asked Questions
Snyk is designed for developers first — it embeds directly into IDEs (VS Code, JetBrains, Eclipse), CI/CD pipelines, and Git workflows, providing real-time security feedback as developers write code. Traditional AppSec tools like Checkmarx and Veracode are primarily for security teams running scans post-development. Snyk’s philosophy is to catch vulnerabilities at the moment of creation rather than after the code is already shipped.
Snyk provides five security products under one platform: Snyk Code (SAST for custom code), Snyk Open Source (SCA for open-source dependencies), Snyk Container (container image scanning), Snyk IaC (infrastructure-as-code security), and Snyk API (dynamic API security testing). All five are included at every pricing tier.
Snyk’s pricing: Free tier covers open-source projects. Team plan is $25/developer/month (minimum 5 developers, up to 10 developers) and includes all five security products with prioritized remediation and compliance reporting. Enterprise plan has custom pricing for larger teams and adds SSO, advanced analytics, SBOM, compliance dashboards, and dedicated support.
DeepCode AI is Snyk’s proprietary AI engine for static application security testing. It uses a hybrid approach combining symbolic AI (pattern-based vulnerability detection) with machine learning trained on billions of lines of code and millions of open-source fixes to find vulnerabilities that rule-based scanners miss. Snyk Agent Fix uses DeepCode AI to generate one-click remediation patches directly in the IDE.
Snyk processes over 1 billion security tests per month across 2,500+ paying customers including Google, Salesforce, Intuit, and Atlassian. The company has raised $530M+ in funding at an $8.6B valuation (2021) and reported $407M+ in revenue in 2025. It was named a Leader in the 2025 Gartner Magic Quadrant for Application Security Testing.
Similar AI Tools to Snyk
View all alternatives of Snyk
Checkmarx
Unified enterprise AppSec with SAST, SCA, DAST and agentic AI security for Fortune 500
Wiz
Agentless cloud security that connects code, cloud, and runtime into one graph
CodeRabbit
The AI control layer for code review, triage, explainability, and security
Ellipsis
AI code review and cloud coding agents — define agents as config, deploy with git push
GitHub Copilot
AI pair programmer for code completion, chat, and autonomous coding agents
Semgrep
Open-source SAST and AI AppSec platform — custom rules, Semgrep Assistant, and Multimodal engine for AI-generated code
Compared with Snyk
Direct head-to-head feature matrices, pricing, and category breakdowns