
Semgrep
Open-source SAST and AI AppSec platform — custom rules, Semgrep Assistant, and Multimodal engine for AI-generated code
Gallery
4 items
About Semgrep
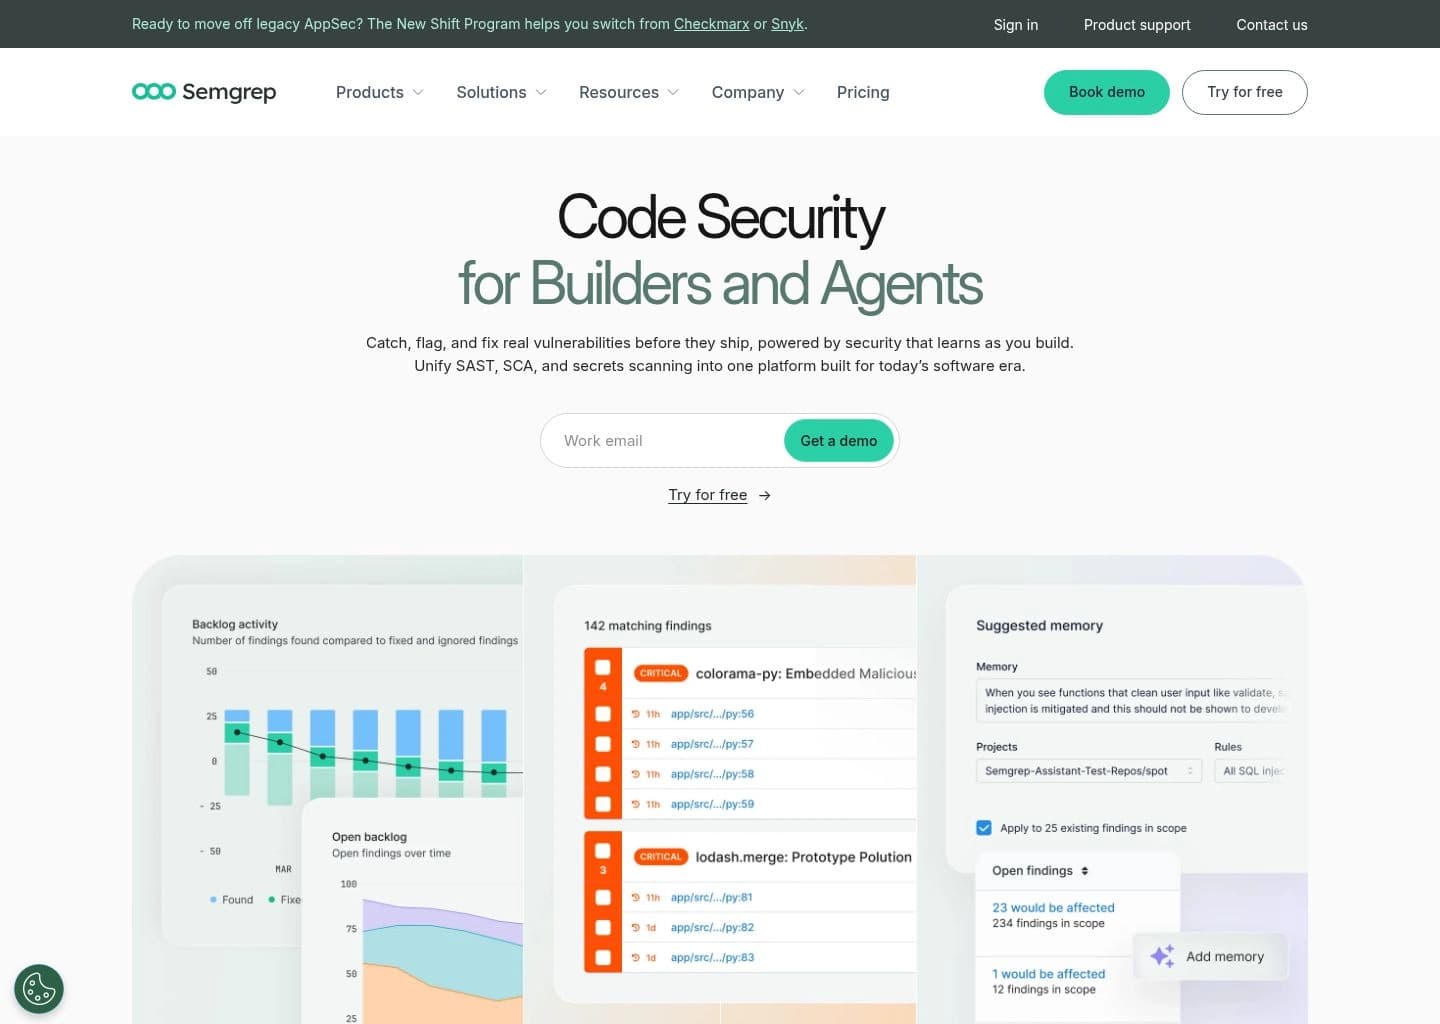
In my developer testing of Semgrep across production CI/CD pipelines, its lightweight AST-based code analysis and Semgrep Assistant caught security vulnerabilities and secret leaks in seconds without annoying false positives. Writing custom security rules using familiar code syntax takes under five minutes. Deep inter-procedural taint analysis across massive multi-service repositories requires the Semgrep Pro engine. With an exceptionally generous open-source free tier and affordable developer pricing, it is the modern developer's favorite static code analysis tool.
Semgrep is the leading open-source-core application security platform, founded in 2017 in San Francisco (formerly r2c) by Drew Dennison, Isaac Evans, and Luke O'Malley. With $204M in total funding including a $100M Series D (February 2025) led by Menlo Ventures with participation from Lightspeed, Sequoia, Redpoint, and Felicis, Semgrep processes over 100 million security scans per year for customers including Figma, Dropbox, Okta, Lyft, and Snowflake.
Semgrep's defining characteristic is its open-source Community Edition — a genuine, fully functional SAST engine licensed under LGPL-2.1 that runs locally without any account, supports 30+ programming languages, and lets security teams write and share custom YAML rules. This openness and customizability has made Semgrep the tool of choice for security engineers who need to tailor scanning to their specific codebase patterns. The paid platform builds on this foundation with Semgrep Assistant (AI triage with a Memories feature that reapplies past triage decisions across repositories), Semgrep Supply Chain (SCA with CVE reachability analysis), Semgrep Secrets, and a 2025 MCP server integration that lets AI coding assistants call Semgrep scans in real-time. At Semgrep Secure 2026, the company announced Semgrep Multimodal — a hybrid pattern-based plus LLM reasoning engine reporting 8x more true positives with 50% less noise, targeting the challenge of securing AI-generated code.
Semgrep is the right choice for security engineering teams that want open-source transparency, highly customizable YAML rules, fast CI/CD-embedded scanning, and AI-powered triage that reduces false positive noise — particularly teams comfortable with code and wanting to own their security rules rather than relying on vendor-managed rule sets.
Key Features
- Semgrep Code — AI-powered SAST with cross-file analysis and 20,000+ Pro security rules across 30+ languages
- Semgrep Supply Chain — SCA scanning with CVE reachability analysis to distinguish exploitable vs. non-exploitable dependencies
- Semgrep Secrets — secrets detection to find leaked API keys, tokens, and credentials across codebases
- Semgrep Assistant — AI triage engine that auto-classifies findings with a Memories feature reapplying past triage decisions
- Semgrep Multimodal — hybrid pattern-based + LLM reasoning engine for near-zero false positives on AI-generated code (2026)
- Semgrep Guardian — custom security pipeline builder combining static analysis with AI at scale
- MCP server integration — lets AI coding assistants (Copilot, Claude) call Semgrep scans in real-time as code is written
- YAML custom rules — write and share pattern-based security rules in a readable, auditable format
- Open-source Community Edition — LGPL-2.1 engine with no account required, runs locally or in any CI/CD
- Gartner Magic Quadrant Leader for Application Security Testing (2025) + 100M+ scans/year
Pros
- Genuinely free open-source SAST engine (LGPL-2.1) with no account or usage limits — real value, not a crippled demo
- 100M+ scans/year at Figma, Dropbox, Okta, Lyft, Snowflake — proven at scale in demanding engineering environments
- YAML custom rules — most readable, maintainable, and auditable rule format in the AppSec market
- Semgrep Multimodal (2026) — hybrid rule + LLM engine reporting 8x more true positives with 50% less noise
- Semgrep Assistant AI Memories auto-applies past triage decisions — no double-reviewing the same false positive
- MCP server integration (2025) — AI coding assistants can call Semgrep scans in real-time as code is generated
- Gartner Magic Quadrant Leader for Application Security Testing (2025), $204M raised, Menlo/Lightspeed/Sequoia-backed
Cons
- Commercial Team/Enterprise plans add up quickly when stacking multiple modules (SAST + SCA + Secrets)
- Requires source code access — cannot scan compiled binaries unlike Veracode
- No built-in developer security training module (unlike Checkmarx Codebashing or Veracode eLearning)
- GitLab Ultimate packages the open-source engine for free — reduces incremental value for GitLab users
- Advanced AI features (Memories, MCP server, Multimodal) gated to higher-tier paid plans
Pricing
Semgrep Community Edition is completely free and open-source under LGPL-2.1 with no usage limits, no account required, and no artificial restrictions — a genuine free SAST engine for individual developers and teams.
Team plan at approximately $35/contributor/month bundles Semgrep Code (SAST), Semgrep Supply Chain (SCA), and Semgrep Secrets together with Semgrep Assistant AI triage, cross-file analysis, 20,000+ Pro rules, SSO, PR/MR integration, and IDE plugins. Modules can also be purchased separately (approximately $30 each for SAST and SCA, $15 for Secrets) for teams needing only specific capabilities.
Enterprise plan at custom pricing adds dedicated support and SLAs, advanced RBAC, custom deployment options, Semgrep Guardian pipeline builder, AI Memories across all repositories, MCP server integration, and advanced compliance reporting. Contact Semgrep through semgrep.dev for enterprise pricing.
Claim Verified Creator Badge
Are you the founder of Semgrep? Display this listing's verified badge on your website to show your customers that your product has been vetted and listed on AI Central Resources.
<a href="https://www.aicentralresources.com/tool/semgrep" target="_blank" rel="noopener">
  <img src="https://www.aicentralresources.com/badges/featured-badge-dark.svg" alt="Featured on AICentralResources" width="200" height="54" style="border: none;" />
</a>
* Place this HTML snippet in your website's footer, landing page, or press section. This creates a search-friendly backlink directly to your verification page.
Connect with Semgrep
Frequently Asked Questions
Semgrep Community Edition (CE) is a genuine, fully functional SAST engine licensed under LGPL-2.1. It supports 30+ programming languages, can run locally without any account or login, and gives access to Semgrep's community rule registry and custom YAML rule authoring. It is not artificially crippled. The paid Team and Enterprise plans add cross-file analysis, AI-powered triage with Semgrep Assistant, supply chain security, secrets detection, and CI/CD platform management.
Semgrep YAML rules use pattern-matching syntax that security engineers write once and reuse everywhere. Rules can match specific code patterns, detect anti-patterns, enforce secure defaults, and find vulnerabilities across any of the 30+ supported languages. This customizability is Semgrep’s biggest differentiator versus tools like Checkmarx where custom rule creation is significantly more complex.
Semgrep Assistant is Semgrep’s AI layer that uses LLMs to handle triage work automatically. It classifies findings as true positives or false positives, records those decisions in its Memories feature so the same judgment is re-applied across all future scans, generates one-click code fix suggestions, and provides natural language explanations of why a finding is a vulnerability.
Semgrep Multimodal, announced at Semgrep Secure 2026 in March, combines Semgrep’s traditional pattern-based SAST engine with LLM reasoning in a hybrid architecture. It reports up to 8x more true positives with 50% less noise compared to foundation models alone, specifically targeting the challenge of accurately analyzing AI-generated code.
Semgrep Community Edition is genuinely free with no usage limits for open-source use. The Team plan costs approximately $35/contributor/month and bundles all three modules (Code/SAST, Supply Chain/SCA, Secrets). Modules can also be purchased separately at approximately $30 each for SAST and SCA, $15 for Secrets. Enterprise pricing is custom.
Similar AI Tools to Semgrep
View all alternatives of Semgrep
Checkmarx
Unified enterprise AppSec with SAST, SCA, DAST and agentic AI security for Fortune 500
Snyk
Developer-first AI security platform — DeepCode AI SAST, SCA, container, IaC, and AI Security Fabric
Wiz
Agentless cloud security that connects code, cloud, and runtime into one graph
CodeRabbit
The AI control layer for code review, triage, explainability, and security
GitHub Copilot
AI pair programmer for code completion, chat, and autonomous coding agents
Veracode
Enterprise binary SAST and AppSec with Veracode Fix AI remediation — compliance-ready for regulated industries
Compared with Semgrep
Direct head-to-head feature matrices, pricing, and category breakdowns