
Cycode
AI-native ASPM platform with Risk Intelligence Graph and ADLC Security for AI-era application security
Gallery
4 items
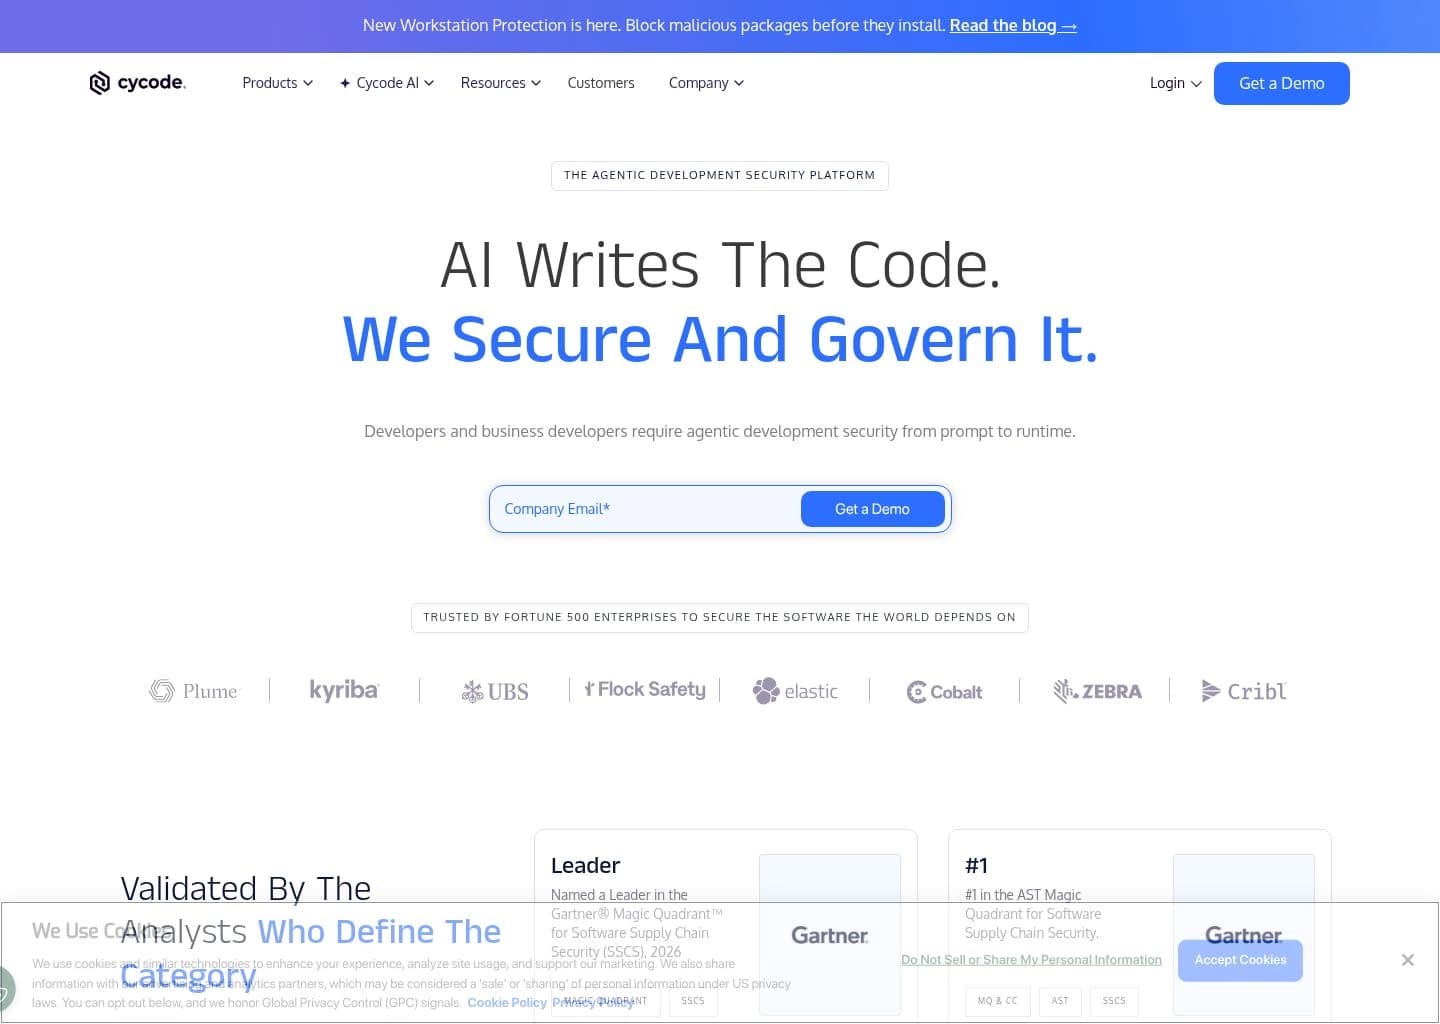
About Cycode
In my DevSecOps testing of Cycode's Application Security Posture Management (ASPM), its Risk Intelligence Graph mapped developer code pipelines, exposed secrets, and misconfigured CI/CD pipelines across GitHub and GitLab in minutes. It correlates developer identities with code risk effortlessly. Large engineering organizations with dozens of third-party plugins require an initial tuning period to suppress duplicate alerts. Priced for modern engineering organizations, it delivers essential governance for securing code from commit to cloud.
Cycode is the leading AI-native Application Security Posture Management (ASPM) platform, founded in 2019 in Tel Aviv by CEO Lior Levy and CTO Ronen Slavin and backed by $81M in funding from Insight Partners and YL Ventures. Named a Leader in the 2026 Gartner Magic Quadrant for Software Supply Chain Security, Cycode is trusted by multiple Fortune 100 companies and serves as the definitive platform for organizations wanting to consolidate fragmented AppSec tool sprawl into a unified, AI-powered security posture.
Cycode\u2019s Complete ASPM platform goes beyond individual scanning tools by providing an end-to-end convergence of Application Security Testing (AST), ASPM orchestration, and Software Supply Chain Security. Its Risk Intelligence Graph (RIG) connects code repositories, CI/CD pipelines, cloud infrastructure, and security scanner outputs into a unified graph that surfaces which vulnerabilities are truly reachable and exploitable in the specific production environment \u2014 not just which ones exist. Maestro AI, Cycode\u2019s AI orchestration engine, reasons across this graph to prioritize findings by business risk, while AI Teammates (the AI Exploitability Agent and AI Fix & Remediation Agent) handle triage and fix generation autonomously. For the AI development era, Cycode\u2019s ADLC Security suite provides AI Visibility, AI Governance, AI Guardrails, AI-BOM, and specialized AI SAST for code generated by AI coding assistants \u2014 addressing the unique vulnerability patterns that AI-generated code introduces. The Cycode MCP Server integrates Cycode\u2019s scanning capabilities directly into AI coding tools.
Cycode is the right choice for enterprise security teams overwhelmed by AppSec tool sprawl, CISOs wanting a unified ASPM control plane across their entire SDLC, and organizations embracing AI-assisted development who need governance and security scanning purpose-built for the AI era.
Key Features
- Complete ASPM — unified Application Security Posture Management consolidating AST, ASPM, and Software Supply Chain Security in one platform
- Risk Intelligence Graph (RIG) — correlates findings across all security tools, code repos, CI/CD, and cloud to identify truly exploitable risks
- Maestro AI — AI orchestration engine that reasons across security findings and prioritizes by business risk and exploitability
- AI Teammates — autonomous AI agents (AI Exploitability Agent, AI Fix & Remediation Agent) that handle security triage and fix automatically
- ADLC Security — AI Development Lifecycle security covering AI Visibility, AI Governance, AI Guardrails, and AI-BOM for AI-generated code
- Cycode MCP Server — integrates Cycode security scanning directly into AI coding assistants like GitHub Copilot and Claude Code
- SAST & AI SAST — static code scanning including specialized detection for AI-generated code vulnerabilities
- CI/CD Security — detects misconfigurations and attacks across GitHub Actions, GitLab CI, Jenkins, and all major pipeline tools
- ASPM Marketplace — 300+ connectors integrating third-party security tools (Snyk, Checkmarx, Wiz, Veracode) into unified posture view
- SBOM & AI-BOM — software and AI bill of materials generation for supply chain transparency and compliance
Pros
- Gartner Magic Quadrant Leader for Software Supply Chain Security (2026) — highest independent analyst validation
- Risk Intelligence Graph correlates findings across all AppSec tools to surface truly exploitable vulnerabilities — eliminates alert noise
- ADLC Security purpose-built for AI-generated code — AI Visibility, AI Governance, AI Guardrails, and AI-BOM in one suite
- Cycode MCP Server integrates directly into AI coding assistants for real-time scan coverage
- 300+ ASPM Marketplace connectors — integrates with Snyk, Checkmarx, Veracode, Wiz, and all major AppSec tools
- AI Teammates autonomously handle exploitability assessment and fix generation — reduces AppSec team burden significantly
- Fortune 100 customer validation — proven in the most demanding enterprise security environments
Cons
- $81M raised — smaller financial backing than Snyk ($530M), Checkmarx ($1.15B acquisition), or Semgrep ($204M)
- Enterprise-only pricing with no self-serve or free tier for evaluation without a sales call
- ASPM consolidation requires integrating existing AppSec tools — complex initial setup for organizations with mature toolchains
- Primarily targets mid-to-large enterprises — may be overkill for small engineering teams
- Newer to market than Checkmarx or Veracode — less legacy customer validation at extreme scale
Pricing
Cycode uses enterprise subscription pricing with no public pricing page and no free tier. All plans require direct engagement with the sales team.
Pricing is based on organizational size, application portfolio, and selected modules within the Complete ASPM platform. Cycode serves Fortune 100 companies and mid-to-large enterprises.
Contact Cycode through cycode.com to request a demo and discuss enterprise pricing. A demo environment is available to qualified organizations.
Claim Verified Creator Badge
Are you the founder of Cycode? Display this listing's verified badge on your website to show your customers that your product has been vetted and listed on AI Central Resources.
<a href="https://www.aicentralresources.com/tool/cycode" target="_blank" rel="noopener">
  <img src="https://www.aicentralresources.com/badges/featured-badge-dark.svg" alt="Featured on AICentralResources" width="200" height="54" style="border: none;" />
</a>
* Place this HTML snippet in your website's footer, landing page, or press section. This creates a search-friendly backlink directly to your verification page.
Connect with Cycode
Frequently Asked Questions
ASPM (Application Security Posture Management) is a category of security tooling that provides a unified, correlated view of an organization's entire application security posture — aggregating findings from SAST, SCA, DAST, container scanning, IaC scanning, and other tools into one platform with AI-powered prioritization, context, and orchestration. Cycode is the leading complete ASPM platform.
Cycode’s Risk Intelligence Graph (RIG) connects all of an organization’s DevOps tools, security scanners, code repositories, CI/CD pipelines, and cloud infrastructure into a unified graph database. This allows Cycode to correlate findings across tools, trace the blast radius of a vulnerability, identify which vulnerabilities are actually reachable and exploitable in the specific environment, and prioritize remediation by business risk rather than raw severity score.
Cycode's ADLC (AI Development Lifecycle) Security suite addresses the unique risks of AI-native software development: AI Visibility maps all AI components in the codebase, AI Governance enforces policies on AI tool and model usage, AI Guardrails prevents AI coding assistants from introducing vulnerabilities, AI-BOM (AI Bill of Materials) inventories every AI model and dataset, and the AI Exploitability Agent assesses the real exploitability of AI-generated code vulnerabilities.
Cycode was Named a Leader in the 2026 Gartner Magic Quadrant for Software Supply Chain Security — the most recent major analyst recognition validating Cycode’s platform approach.
Cycode acquired Bearer in March 2024 — a developer-first SAST and API security tool focused on privacy-by-design and data flow analysis. Bearer’s capabilities were integrated into Cycode’s Complete ASPM platform, strengthening its SAST and data security scanning capabilities.
Similar AI Tools to Cycode
View all alternatives of Cycode
Checkmarx
Unified enterprise AppSec with SAST, SCA, DAST and agentic AI security for Fortune 500
Snyk
Developer-first AI security platform — DeepCode AI SAST, SCA, container, IaC, and AI Security Fabric
Semgrep
Open-source SAST and AI AppSec platform — custom rules, Semgrep Assistant, and Multimodal engine for AI-generated code
Veracode
Enterprise binary SAST and AppSec with Veracode Fix AI remediation — compliance-ready for regulated industries
Wiz
Agentless cloud security that connects code, cloud, and runtime into one graph
Orca Security
Agentless CNAPP with patented SideScanning — 100% cloud coverage without installing a single agent
Compared with Cycode
Direct head-to-head feature matrices, pricing, and category breakdowns