
Splunk
World\u2019s leading enterprise SIEM — SPL, 2,800+ Splunkbase apps, ESCU detection content, now part of Cisco
Gallery
4 items
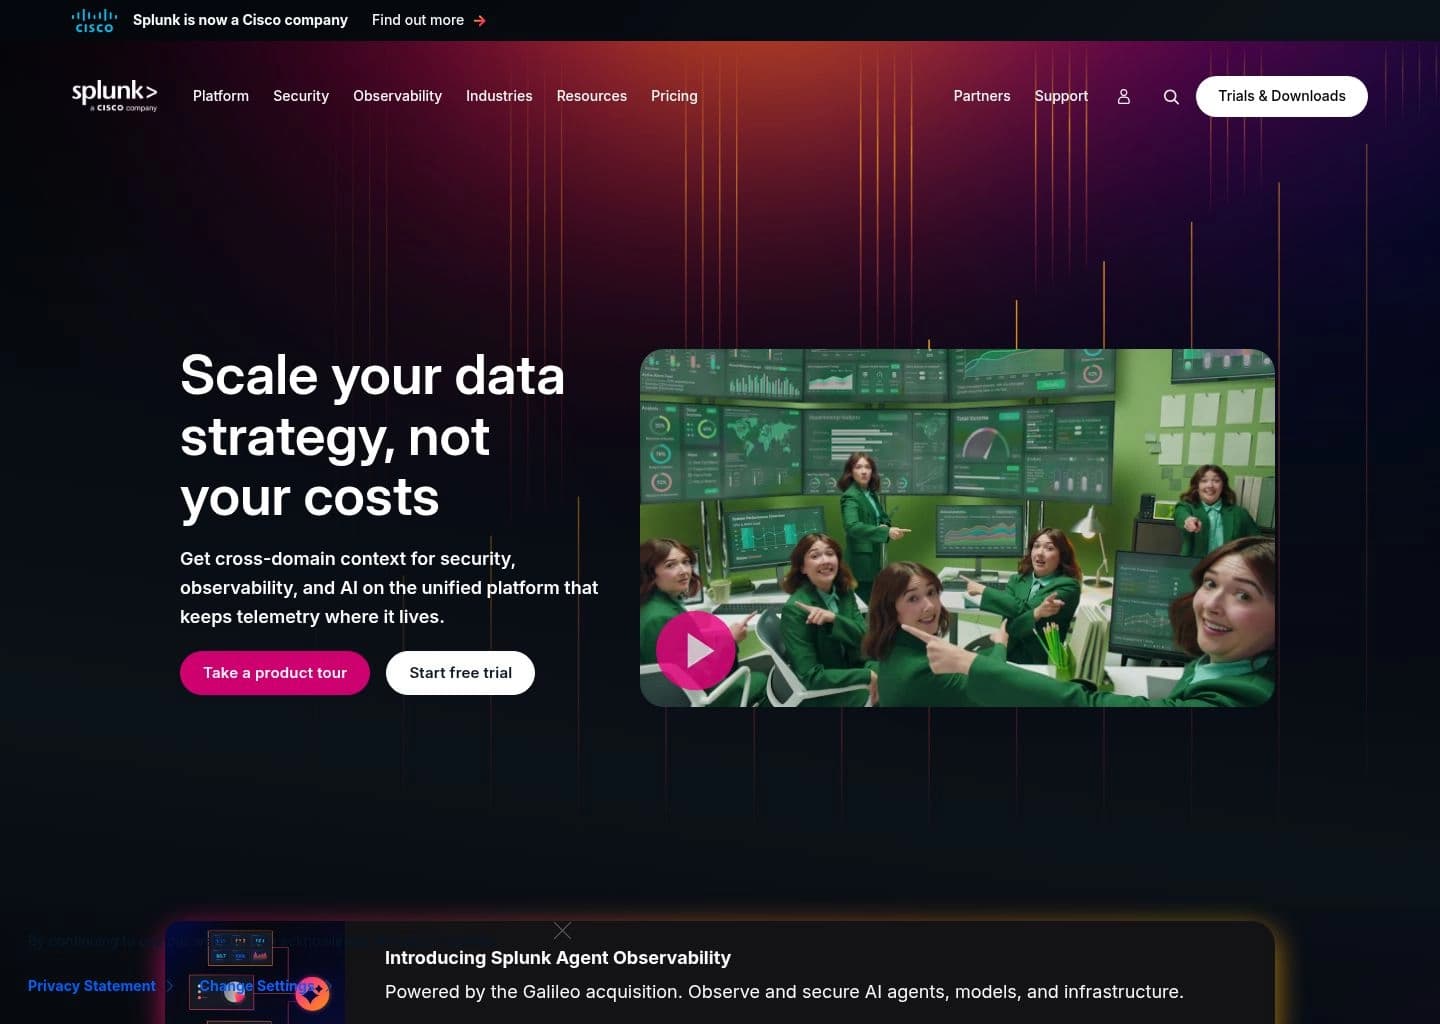
About Splunk
Having engineered enterprise security pipelines inside Splunk Enterprise Security, its Search Processing Language (SPL) and vast app ecosystem indexed hundreds of terabytes of machine data daily, powering complex enterprise SOC investigations with surgical precision. Its visualization dashboards are second to none. Data ingestion-based pricing can become astronomical for high-volume logging environments without rigorous data pipeline filtering. Now part of Cisco, it remains the undisputed heavyweight titan of enterprise SIEM and security observability.
Splunk is the world\u2019s most established enterprise SIEM and machine data analytics platform, founded in 2003 in San Francisco and acquired by Cisco in March 2024 for $28 billion \u2014 the largest cybersecurity acquisition in history. With 15,000+ enterprise customers, $3.7B pre-acquisition ARR, and 2,800+ Splunkbase marketplace apps representing 15+ years of community-built detection content, Splunk Enterprise Security is the gold standard SIEM for large SOCs, regulated industries, and organizations with complex multi-source detection requirements.
Splunk\u2019s core platform ingests machine data from any source \u2014 endpoints, firewalls, cloud services, applications, and network devices \u2014 making it searchable, correlatable, and actionable via SPL (Search Processing Language), Splunk\u2019s powerful proprietary query language. Splunk Enterprise Security adds the SIEM layer with real-time correlation, Risk-Based Alerting (RBA) to reduce alert fatigue, and the ESCU (Enterprise Security Content Updates) package of MITRE ATT&CK-mapped detection rules maintained by Splunk Security Research. Splunk SOAR provides security orchestration and automation with 300+ pre-built playbooks. Post-Cisco acquisition, Cisco AI Assistant for Security provides natural-language GenAI investigation capabilities. The Splunkbase marketplace with 2,800+ apps \u2014 covering integrations with CrowdStrike, Palo Alto, Microsoft, and every major vendor \u2014 is Splunk\u2019s biggest competitive moat.
Splunk is the right choice for large enterprise SOCs, government agencies, financial services organizations, and regulated industries with high data volumes (500+ GB/day), dedicated SIEM engineering teams with SPL expertise, complex compliance requirements (FedRAMP, HIPAA, PCI-DSS, SOX), and the budget to support one of the most powerful but also most expensive SIEM platforms in the market.
Key Features
- Splunk Enterprise Security (SIEM) — industry-leading security information and event management with real-time correlation and investigation
- SPL (Search Processing Language) — powerful proprietary query language for custom detection, hunting, and visualization
- ESCU (Enterprise Security Content Updates) — continuously updated MITRE ATT&CK-mapped detection rule packs from Splunk Security Research
- Splunk SOAR — security orchestration, automation, and response platform with 300+ pre-built playbooks
- Splunkbase marketplace — 2,800+ apps covering integrations, detection content, and dashboards built over 15+ years
- Cisco AI Assistant for Security — GenAI analyst integrated into Splunk post-Cisco acquisition for natural-language investigation
- Risk-Based Alerting (RBA) — aggregates risk scores across entities to reduce alert fatigue dramatically
- Splunk Observability Suite — unified IT and security observability for infrastructure, applications, and logs
- Flexible deployment — cloud (Splunk Cloud), on-premises (Splunk Enterprise), or hybrid deployments
- FedRAMP authorized — approved for US federal government and regulated industry deployments
Pros
- Gold standard enterprise SIEM — 15,000+ customers, $3.7B pre-acquisition ARR, 15+ years of proven production deployments
- 2,800+ Splunkbase apps — unmatched ecosystem with detection content, integrations, and dashboards built over 15+ years
- ESCU MITRE ATT&CK detection packs — hundreds of continuously updated, community-validated detection rules
- SPL is the most powerful SIEM query language — enables complex custom detections that simpler SIEM tools cannot replicate
- Risk-Based Alerting reduces alert fatigue significantly by aggregating risk scores across entities
- Cisco AI Assistant for Security post-acquisition adds GenAI investigation capabilities
- FedRAMP authorized — approved for US federal and highly regulated industry deployments
Cons
- Per-GB/day pricing is the most expensive SIEM model — 500 GB/day deployments run $788K-$2.5M/year
- SPL (Search Processing Language) has a steep learning curve requiring specialized analyst expertise
- Cisco acquisition (March 2024) created product roadmap uncertainty for existing customers
- Heavy infrastructure and tuning requirements — not suitable for small teams without dedicated SIEM engineers
- Microsoft Sentinel and Google Chronicle are increasingly competitive at lower cost for cloud-native organizations
Pricing
Splunk uses a per-GB/day data ingestion pricing model — the most comprehensive but also most expensive SIEM pricing model available.
Splunk base platform: approximately $150-$225/GB/day. Splunk Enterprise Security (SIEM add-on): approximately $250-$400/GB/day. A 500 GB/day organization can expect annual costs of $788,000 to $2.5 million at list pricing before volume discounts.
Workload-based pricing is available as an alternative for high-volume organizations, licensing by compute workload rather than data volume. Splunk Cloud (SaaS), Splunk Enterprise (on-premises), and hybrid deployments all supported.
Splunk Free provides 500 MB/day ingestion for non-production use. A Developer License provides 5 GB/day at no cost for development environments. A 60-day trial is available. Contact Cisco/Splunk through splunk.com for enterprise pricing and volume discount discussions.
Claim Verified Creator Badge
Are you the founder of Splunk? Display this listing's verified badge on your website to show your customers that your product has been vetted and listed on AI Central Resources.
<a href="https://www.aicentralresources.com/tool/splunk" target="_blank" rel="noopener">
  <img src="https://www.aicentralresources.com/badges/featured-badge-dark.svg" alt="Featured on AICentralResources" width="200" height="54" style="border: none;" />
</a>
* Place this HTML snippet in your website's footer, landing page, or press section. This creates a search-friendly backlink directly to your verification page.
Connect with Splunk
Frequently Asked Questions
Cisco completed its $28 billion acquisition of Splunk in March 2024 — the largest cybersecurity acquisition in history. Splunk now operates as part of Cisco's security portfolio alongside Cisco XDR, Cisco Talos threat intelligence, and Cisco's networking products. The acquisition aims to combine Cisco's network telemetry with Splunk's SIEM and observability capabilities for unified threat prediction and prevention.
SPL (Search Processing Language) is Splunk’s proprietary query language for searching, correlating, and visualizing machine data. It is extremely powerful and flexible, allowing security analysts to write custom detections, build dashboards, and create complex correlation rules. However, it requires significant training and is one of the main reasons Splunk favors large SOCs with dedicated analyst teams over smaller organizations.
Splunk’s primary pricing model is per GB of data ingested per day. The base Splunk platform costs approximately $150-$225/GB/day; Splunk Enterprise Security (the SIEM layer) is priced at approximately $250-$400/GB/day. A 500 GB/day organization can expect annual costs of $788,000 to $2.5 million. Workload-based pricing is available as an alternative for high-volume organizations. Volume discounts apply at scale.
Splunkbase is Splunk’s app marketplace with 2,800+ apps covering integrations with every major security vendor, industry-specific detection content, visualization dashboards, and specialized tools. The ESCU (Enterprise Security Content Updates) package ships hundreds of MITRE ATT&CK-mapped detection rules. This ecosystem is Splunk’s biggest moat — 15+ years of community-built content that no competing SIEM has replicated.
Splunk Enterprise Security is best suited for large enterprises and government organizations with dedicated SOC teams, 500+ GB/day data volumes, existing SPL expertise, compliance requirements (FedRAMP, HIPAA, PCI-DSS, SOX), and complex multi-source detection needs. Mid-market organizations without SPL expertise or large data volumes often find Microsoft Sentinel or Exabeam more cost-effective.
Similar AI Tools to Splunk
View all alternatives of Splunk
Microsoft Sentinel
Cloud-native SIEM+SOAR on Azure — AI threat detection, KQL hunting, and native M365 integration
Exabeam
AI-native SecOps platform with UEBA, Nova AI agents, and Agent Behavior Analytics for the agentic enterprise
Darktrace
Self-Learning AI cybersecurity — detects zero-day and insider threats without signatures across 7 domains
IBM QRadar SIEM
IBM's AI-powered on-premises SIEM — 30+ years of threat detection with watsonx GenAI investigation
CrowdStrike Falcon
World\u2019s leading AI-native cybersecurity platform — Charlotte AI, EDR/XDR, and $5.25B ARR on one Falcon agent
SentinelOne
Autonomous AI XDR with offline EDR, one-click ransomware rollback, Purple AI, and 100% MITRE coverage
Compared with Splunk
Direct head-to-head feature matrices, pricing, and category breakdowns