
Top 15 Best Microsoft Defender for Endpoint Alternatives in 2026
Editorial analysis comparing key features, free tier limits, pricing spectrums, and real-world trade-offs.
Executive Summary & Buying Decision
We benchmarked 5+ leading alternative tools competing with Microsoft Defender for Endpoint across feature depth, pricing transparency, and workflow efficiency. Pricing options range from starter tiers to enterprise plans around $2.46 – $30/mo. Choose Microsoft Defender for Endpoint for Enterprises on Microsoft 365 E5 and Azure needing native EDR/XDR with zero incremental cost, unified Defender XDR portal, Copilot for Security AI, and deep Windows/M365/Intune integration, or select CrowdStrike Falcon for complementary capabilities.
Baseline Tool Overview
Microsoft Defender for Endpoint
Enterprise EDR/XDR with Copilot for Security — native M365 integration, Defender XDR portal, free in M365 E5
Enterprises on Microsoft 365 E5 and Azure needing native EDR/XDR with zero incremental cost, unified Defender XDR portal, Copilot for Security AI, and deep Windows/M365/Intune integration
- Pricing Model:Paid
- Starting Price:$3/user/mo
- Free Tier / Limits:No free plan; Plan 1 from $3/user/month; Plan 2 from $5.20/user/month; included in M365 E5 at no incremental cost
- Defender XDR unified portal — correlates endpoint, email, identity, cloud apps, and cloud signals into single cross-domain incident view
- Automated Investigation and Response (AIR) — AI-driven autonomous triage, investigation, and remediation
- Copilot for Security — GenAI SOC assistant for incident summarization, script deobfuscation, and natural-language threat hunting
- Behavioral AI detection — ML models detect threats by behavior patterns not signatures
Top Recommendations by Use Case
CrowdStrike Falcon
Leading direct competitor in this category offering proven performance and strong feature maturity.
SentinelOne
Provides generous free capabilities for individual developers and creators with zero upfront cost.
Checkmarx
Comprehensive multi-feature platform covering end-to-end workflows.
Why Teams Migrate from Microsoft Defender for Endpoint
Cost & Plan Scalability
Users evaluating alternatives to Microsoft Defender for Endpoint to optimize subscription costs or access more flexible tiers.
Advanced Automation & Feature Depth
Teams seeking deeper automation and specialized functionality tailored to specific project requirements.
Delivers comprehensive capabilities designed for high-throughput workflows.
Compare vs CrowdStrike Falcon
Ecosystem & Integration Compatibility
Organizations requiring seamless integration with their existing software stack and team tools.
Features robust multi-platform compatibility and enterprise security standards.
Compare vs WizHead-to-Head Comparison Matrix
| Software Tool | Pricing Model | Free Tier Scope | Target Persona / Best For | Rating | Head-to-Head |
|---|---|---|---|---|---|
 Microsoft Defender for EndpointBaseline | Paid ($3/user/mo) | No free plan; Plan 1 from $3/user/month; Plan 2 from $5.20/user/month; included in M365 E5 at no incremental cost | Enterprises on Microsoft 365 E5 and Azure needing native EDR/XDR with zero incremental cost, unified Defender XDR portal, Copilot for Security AI, and deep Windows/M365/Intune integration | 4.8 | Full Review |
Paid (Custom) | 15-day free trial of Falcon platform with NGAV, device control, and mobile device protection; no credit card required | Enterprise and mid-market security teams consolidating endpoint protection, identity security, cloud security, SIEM, and SOC operations onto a single AI-native platform with Charlotte AI agentic automation | 4.8 | Compare | |
Paid (Custom) | No permanent free plan; 30-day free trial available; pricing starts from ~$69.99/device/year (Core tier) | Enterprise and mid-market security teams needing autonomous on-device AI EDR/XDR that works offline, one-click ransomware rollback, and a unified platform spanning endpoint, identity, cloud, and SIEM | 4.8 | Compare | |
Enterprise (Custom Enterprise Contract (priced per cloud workload / VM / container scale)) | Custom enterprise architecture review, cloud risk assessment, and live multi-cloud demo | Enterprise CISOs, DevSecOps teams, and cloud security architects protecting complex multi-cloud infrastructure, preventing data breaches, and ensuring continuous compliance | 4.8 | Compare | |
Enterprise (Custom) | No free plan; enterprise contracts required; free trial and demo available through sales team | Large enterprises and regulated organizations needing comprehensive unified application security testing across SAST, SCA, DAST, API, IaC, and supply chain with proven Fortune 500 deployment at scale | 4.8 | Compare |
Deep-Dive Alternative Profiles
Click any tool card to expand its complete interface & pricing evaluation
World\u2019s leading AI-native cybersecurity platform — Charlotte AI, EDR/XDR, and $5.25B ARR on one Falcon agent
CrowdStrike Falcon focuses on "World\u2019s leading AI-native cybersecurity platform — Charlotte AI, EDR/XDR, and $5.25B ARR on one Falcon agent", providing an agile and dedicated approach compared to Microsoft Defender for Endpoint.
Key Capabilities
- Falcon Insight XDR — industry-leading EDR and XDR with 1-second telemetry visibility across all endpoints
- Charlotte AI — generative AI security analyst for natural-language threat investigation and agentic SOC automation
- Falcon Prevent — AI-powered next-generation antivirus (NGAV) with behavioral analysis and exploit mitigation
- Falcon Identity Protection — real-time identity threat detection and response with FalconID phishing-resistant MFA
Pricing & Best Match
Autonomous AI XDR with offline EDR, one-click ransomware rollback, Purple AI, and 100% MITRE coverage
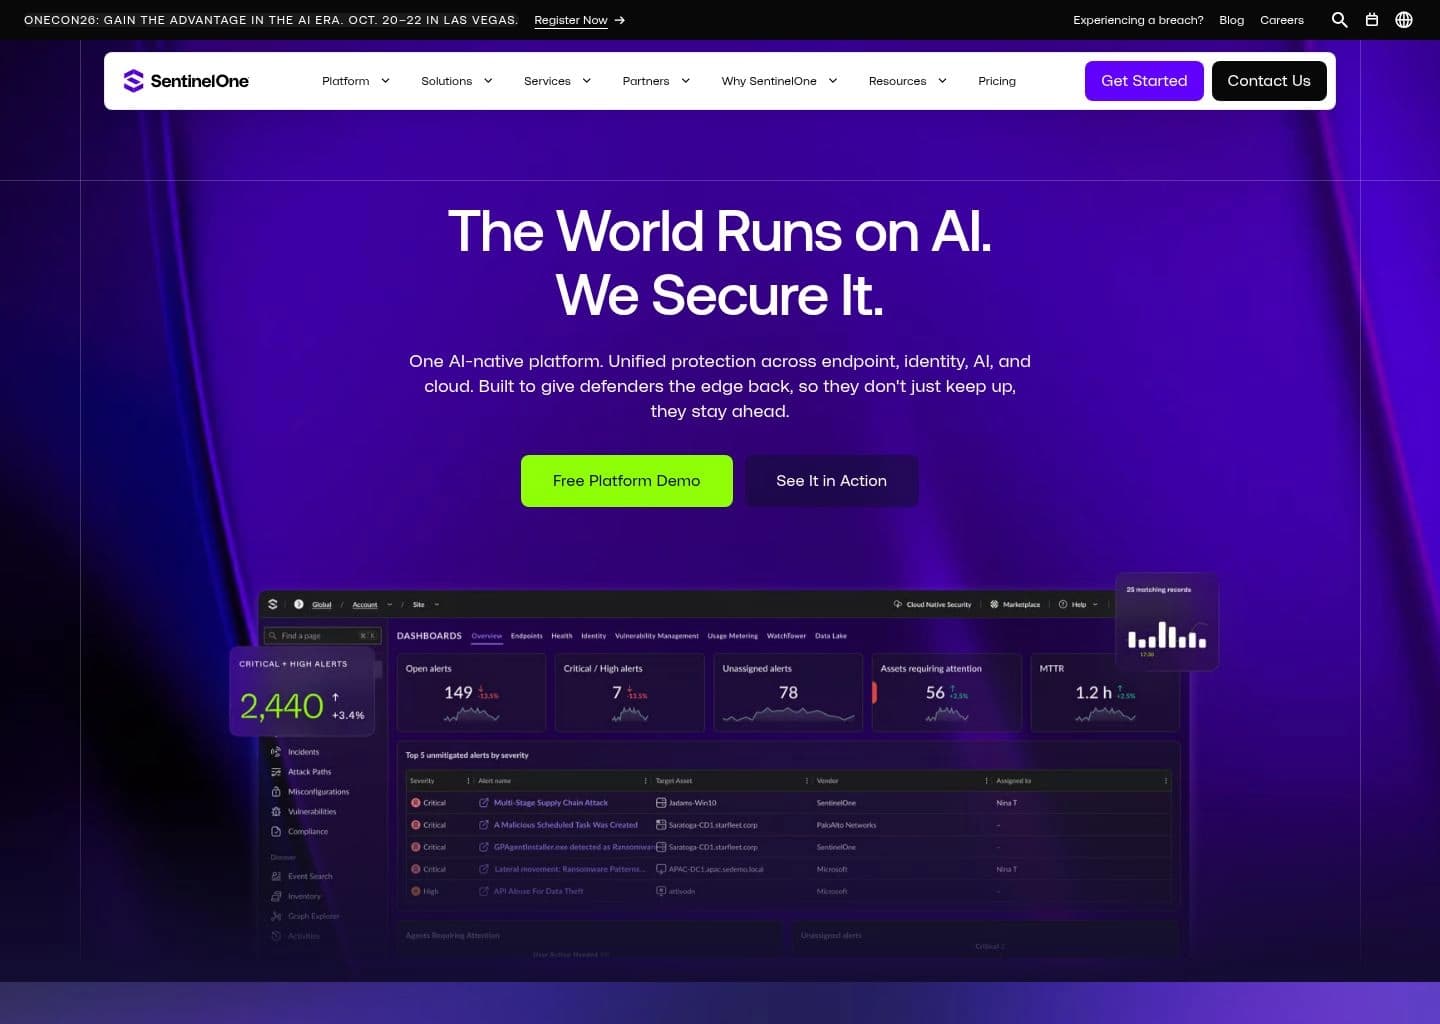
SentinelOne focuses on "Autonomous AI XDR with offline EDR, one-click ransomware rollback, Purple AI, and 100% MITRE coverage", providing an agile and dedicated approach compared to Microsoft Defender for Endpoint.
Key Capabilities
- Autonomous on-device AI — threat detection and response runs locally on the endpoint, protecting even offline or air-gapped devices
- Storyline ActiveEDR — automatically correlates all related events into a single visual attack narrative for instant investigation
- Purple AI — GenAI security analyst with natural-language threat hunting and agentic autonomous investigation (included from Complete tier)
- One-click ransomware rollback — restores encrypted or deleted files to pre-attack state using VSS shadow copies
Pricing & Best Match
AI-native ASPM platform with Risk Intelligence Graph and ADLC Security for AI-era application security
Deep learning AI endpoint security with CryptoGuard, Synchronized Security, and 24/7 MDR for mid-market
AI-powered XDR with cross-layer telemetry, AgentiX AI agents, and the path to Cortex XSIAM AI SOC
Cloud-native SIEM+SOAR on Azure — AI threat detection, KQL hunting, and native M365 integration
World\u2019s leading enterprise SIEM — SPL, 2,800+ Splunkbase apps, ESCU detection content, now part of Cisco
AI-native SecOps platform with UEBA, Nova AI agents, and Agent Behavior Analytics for the agentic enterprise
Self-Learning AI cybersecurity — detects zero-day and insider threats without signatures across 7 domains
IBM's AI-powered on-premises SIEM — 30+ years of threat detection with watsonx GenAI investigation
Human Risk Management platform — email security, collaboration, insider risk, and AI governance
World's largest enterprise email security platform — threat protection, DLP, compliance, and AI governance in one
AI-native behavioral email security — stops BEC, phishing, and account takeover that gateways miss
Frequently Asked Questions
CrowdStrike Falcon is one of the top alternatives to Microsoft Defender for Endpoint, offering strong feature parity and active development.
Know another alternative to Microsoft Defender for Endpoint?
Help the community by submitting other similar tools you've used. Your contribution helps others make better decisions.