
SentinelOne
Autonomous AI XDR with offline EDR, one-click ransomware rollback, Purple AI, and 100% MITRE coverage
Gallery
4 items
About SentinelOne
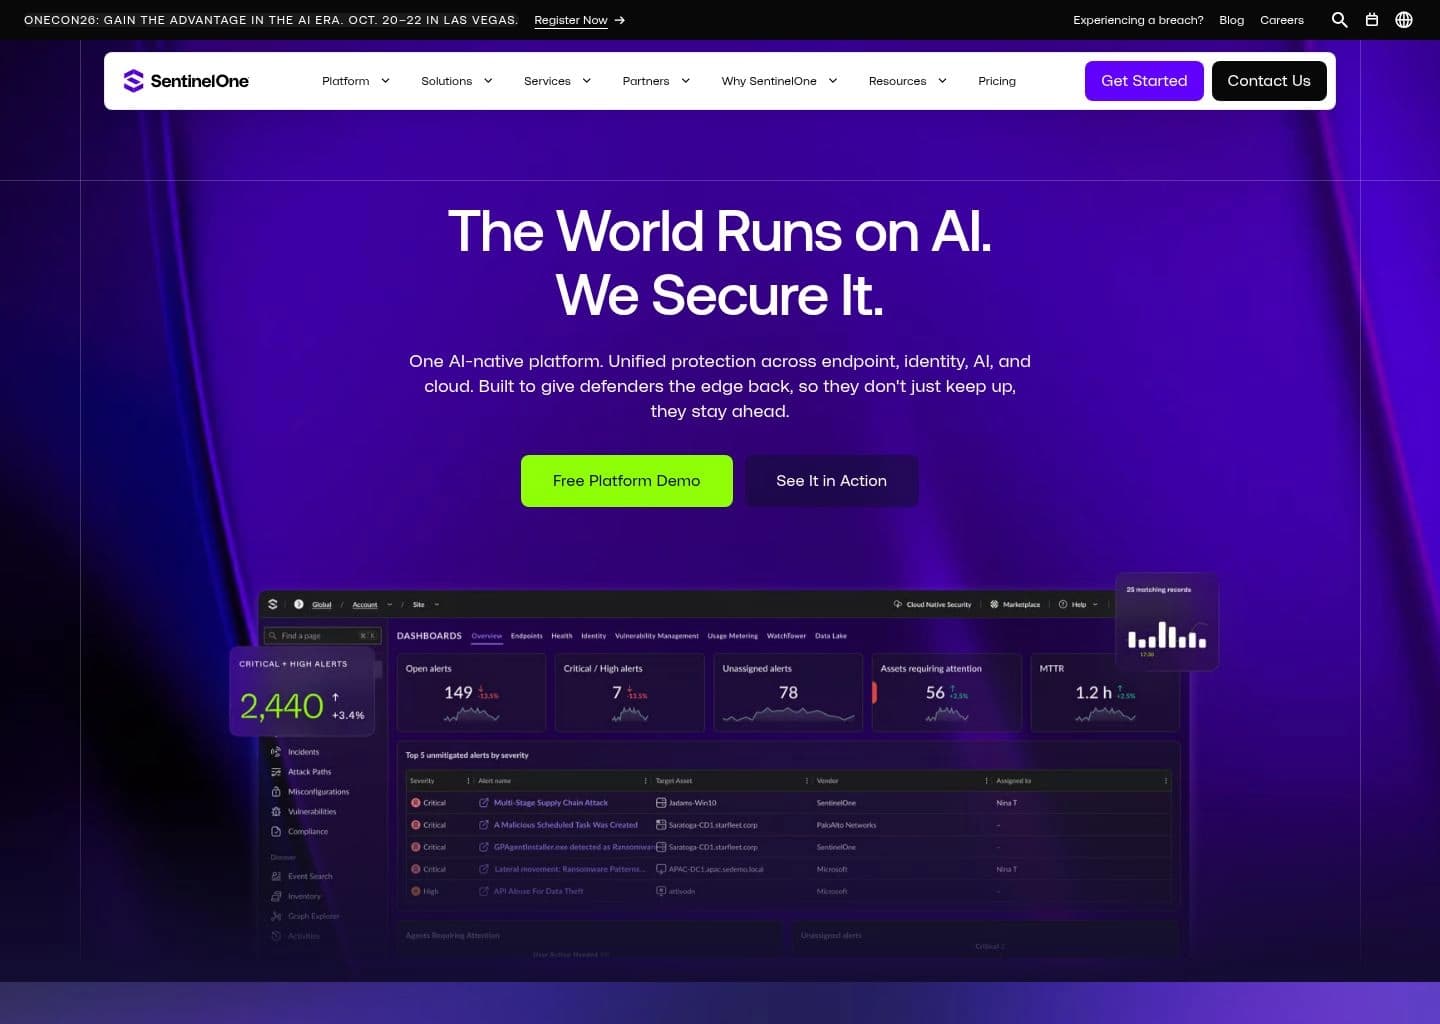
Having tested SentinelOne Singularity across simulated ransomware attacks, its autonomous on-agent behavioral AI detected encryption attempts and executed a 1-click system rollback to restore compromised files in seconds—even offline without internet connectivity. Purple AI streamlines complex threat hunting. The centralized console features extensive administrative controls that require enterprise SOC onboarding to configure properly. Achieving 100% detection across MITRE ATT&CK evaluations, it is an elite choice for enterprise autonomous endpoint security.
SentinelOne is an AI-native autonomous cybersecurity company founded in 2013 by Tomer Weingarten, Almog Cohen, and Ehud Shamir in Tel Aviv, now headquartered in Mountain View, California and traded on NYSE (S). With $1.001 billion in FY2026 revenue and $1.055 billion in ARR (Q3 FY2026), both growing approximately 22-24% year-over-year, SentinelOne crossed its $1 billion annual revenue milestone for the first time and serves 1,572 customers with $100K+ ARR across approximately 2,700 employees worldwide.
SentinelOne\u2019s defining technical differentiation is its autonomous, on-device AI architecture: unlike cloud-dependent EDR platforms, SentinelOne\u2019s AI models run directly on the endpoint, enabling threat detection and response even when devices are offline or disconnected from the internet. Storyline ActiveEDR automatically correlates all related security events into a visual attack narrative, eliminating manual investigation. One-click ransomware rollback restores encrypted files to their pre-attack state via Windows VSS shadow copies. Purple AI \u2014 the first GenAI analyst natively integrated into an XDR platform (2024) \u2014 translates natural-language queries into threat hunting searches and supports agentic autonomous investigation, included from the Complete tier. SentinelOne achieved 100% MITRE ATT&CK detection coverage in 2024 evaluations with zero delayed detections. The Singularity platform spans endpoint (EDR/XDR), identity (Attivo Networks), cloud workload security (PingSafe/CNAPP), AI-SIEM, and Vigilance MDR managed service in one unified agent.
SentinelOne is the right choice for security teams wanting autonomous AI that works offline, organizations prioritizing one-click ransomware recovery, and enterprises seeking a single platform spanning EDR, XDR, identity, cloud, and managed detection without CrowdStrike\u2019s cloud dependency.
Key Features
- Autonomous on-device AI — threat detection and response runs locally on the endpoint, protecting even offline or air-gapped devices
- Storyline ActiveEDR — automatically correlates all related events into a single visual attack narrative for instant investigation
- Purple AI — GenAI security analyst with natural-language threat hunting and agentic autonomous investigation (included from Complete tier)
- One-click ransomware rollback — restores encrypted or deleted files to pre-attack state using VSS shadow copies
- Singularity XDR — unified telemetry across endpoints, cloud workloads, identities, and network for cross-domain detection
- Singularity AI-SIEM — AI-native SIEM with real-time data pipelines and autonomous correlation
- Singularity Identity — identity threat detection and response via Attivo Networks acquisition
- Singularity Cloud Security — CNAPP and cloud workload protection via PingSafe acquisition
- Vigilance MDR — 24/7 managed detection and response service layered on Singularity platform
- 100% MITRE ATT&CK detection coverage — achieved in 2024 evaluations with zero delayed detections
Pros
- Autonomous on-device AI — detection and response continues even when endpoints are offline or air-gapped
- One-click ransomware rollback via VSS — restores encrypted files instantly without manual intervention
- 100% MITRE ATT&CK detection coverage (2024) — best-in-class independent detection benchmark result
- Storyline ActiveEDR auto-correlates attack events into visual narratives — eliminates manual investigation
- Purple AI (first LLM natively in XDR) — natural-language threat hunting and agentic investigation from Complete tier
- $1.001B FY2026 revenue, $1.055B ARR — proven scale with 22-24% YoY growth on NYSE
- Unified platform: endpoint + identity (Attivo) + cloud (PingSafe) + AI-SIEM + MDR in one agent
Cons
- Pricing is largely quote-based at higher tiers — harder to budget upfront vs CrowdStrike’s published list pricing
- EDR, data retention, Storyline, and Purple AI only available from the Complete tier ($179.99/device/yr) and above
- Still GAAP unprofitable despite $1B+ ARR — -$451M GAAP net loss in FY2026
- Advanced features require significant SOC expertise to fully leverage
- Cross-platform macOS/Linux coverage is less mature than Windows in some edge cases
Pricing
SentinelOne offers five pricing tiers based on per-endpoint annual licensing:
Singularity Core: ~$69.99/device/year \u2014 EPP and basic endpoint protection. Singularity Control: $79.99/device/year \u2014 adds firewall management, device control, and cloud workload protection. Singularity Complete: $179.99/device/year \u2014 adds full EDR, XDR, Storyline, Purple AI, and 14-day data retention. Singularity Commercial: $229.99/device/year \u2014 adds identity threat detection, managed threat hunting, and 90-day data retention. Singularity Enterprise: custom pricing \u2014 adds agentic AI SOC analyst, full forensics, and 24/7 MDR.
Starting price is approximately $5.83/endpoint/month. Enterprise pricing is custom-quoted via the sales team. Vigilance MDR can be added as a managed service layer on any tier. A 30-day free trial is available.
Claim Verified Creator Badge
Are you the founder of SentinelOne? Display this listing's verified badge on your website to show your customers that your product has been vetted and listed on AI Central Resources.
<a href="https://www.aicentralresources.com/tool/sentinelone" target="_blank" rel="noopener">
  <img src="https://www.aicentralresources.com/badges/featured-badge-dark.svg" alt="Featured on AICentralResources" width="200" height="54" style="border: none;" />
</a>
* Place this HTML snippet in your website's footer, landing page, or press section. This creates a search-friendly backlink directly to your verification page.
Connect with SentinelOne
Frequently Asked Questions
Purple AI is SentinelOne’s generative AI security analyst built into the Singularity platform, included from the Complete tier. It translates natural-language queries into PowerQuery threat hunting searches, auto-generates investigation summaries, and supports agentic autonomous investigation workflows. Purple AI was the first LLM natively integrated into an XDR platform when it launched in 2024.
SentinelOne’s autonomous AI engine runs directly on the endpoint device, not in the cloud. This means threat detection and response continues even when the endpoint is offline or disconnected from the internet. CrowdStrike Falcon, by contrast, is primarily cloud-dependent for its detection logic — a meaningful architectural difference for air-gapped or remote environments.
SentinelOne’s one-click rollback feature uses Windows Volume Shadow Copies (VSS) to restore encrypted or corrupted files to their pre-attack state in seconds after a ransomware attack is detected and blocked. This automated rollback capability is included in the Singularity Complete tier and above.
SentinelOne pricing has five tiers: Core (~$69.99/device/yr), Control ($79.99/device/yr), Complete ($179.99/device/yr — includes EDR, XDR, Purple AI), Commercial ($229.99/device/yr — adds identity threat detection and managed threat hunting), and Enterprise (custom). Starting price is approximately $5.83/endpoint/month.
SentinelOne achieved $1.001 billion in FY2026 revenue (ended January 31, 2026), up 22% year-over-year, crossing the $1 billion revenue milestone for the first time. ARR reached $1.055 billion (Q3 FY2026). The company is traded on NYSE under ticker S with approximately 2,700 employees.
Similar AI Tools to SentinelOne
View all alternatives of SentinelOne
CrowdStrike Falcon
World\u2019s leading AI-native cybersecurity platform — Charlotte AI, EDR/XDR, and $5.25B ARR on one Falcon agent
Wiz
Agentless cloud security that connects code, cloud, and runtime into one graph
Checkmarx
Unified enterprise AppSec with SAST, SCA, DAST and agentic AI security for Fortune 500
Cycode
AI-native ASPM platform with Risk Intelligence Graph and ADLC Security for AI-era application security
Snyk
Developer-first AI security platform — DeepCode AI SAST, SCA, container, IaC, and AI Security Fabric
Microsoft Defender for Endpoint
Enterprise EDR/XDR with Copilot for Security — native M365 integration, Defender XDR portal, free in M365 E5
Compared with SentinelOne
Direct head-to-head feature matrices, pricing, and category breakdowns